

Too many bugs are reaching production.
QA & Testing
Outsource QA to a team that owns release confidence.
NetForemost adds nearshore QA capacity to your delivery team: fewer production bugs, wider test coverage, validated releases, and a clear QA process across ongoing and fixed-scope projects.
Quality assurance workflowActive
- Discovery
- 02Test Planning
- 03Test Cases
- 04Manual QA
- 05Regression Testing
- 06Bug Reporting
- 07Release Validation
On this page13 sections
- What this service helps you solve
- When to outsource QA, when to hire, and when to do neither
- Embedded or managed
- What outsourced QA covers
- What the engagement includes
- Tools and CI
- Coverage and reporting
- How an engagement starts
- Roles that may support this service
- How we engage: three nearshore models
- Discovery
- QA case studies and guides
- Questions about this service
Why teams come to us
What this service helps you solve
Your team does not have a clear QA process.
Releases feel risky, rushed, or unstable.
Developers are spending too much time finding and reproducing issues.
Regression testing is inconsistent, undocumented, or missing.
You need QA capacity without building a full internal QA team.
Decision guide
When to outsource QA, when to hire, and when to do neither
Outsourcing QA is not always the right answer. Here is how we would tell you which of the three you are looking at.
Outsource when quality is a delivery constraint, not a headcount plan
You are shipping, defects are reaching production, and the team is absorbing the cost in rework and interrupted sprints. You need coverage now, and a QA hire is months away from being productive even if you start today. This is the case outsourcing is built for: capacity that is useful quickly, on a commitment you can end.
Hire when QA is becoming a permanent function with institutional memory
If testing is already continuous, the product is stable, and the work is increasingly about owning quality culture rather than covering a gap, an in house QA lead will beat any vendor. Depth of product knowledge compounds, and that is the one thing an external team builds more slowly.
Do neither, yet, when the problem is upstream
If defects trace back to unclear requirements, no definition of done, or a release process nobody trusts, more testing will find more bugs without shipping anything faster. Fix the process first. We will tell you when that is what we are seeing, because selling you QA that cannot work is a bad trade for both of us.
How we engage
Embedded QA or a managed QA function
Both give you the same engineers and the same standards. The difference is who owns the quality decision, and it is usually settled by whether you already have a delivery process worth joining.
| Embedded QA | Managed QA function | |
|---|---|---|
| Best when | You have a delivery team and a process, and the gap is testing capacity | You have no QA function, or quality has no clear owner |
| Who owns release confidence | Your team. We supply the testing and the evidence | We do, against criteria we agree with you |
| How the team works | Inside your sprints, your board, your ceremonies | As a QA function with its own cadence, reporting into your releases |
| What you manage | The engineers, the same as any team member | The outcome. We manage the engineers |
| Test strategy | Yours, and we work to it | Ours to propose, yours to approve |
| Scaling | Add or remove engineers | Change the scope of the function |
| Typical starting point | One or two QA engineers | A lead plus engineers, sized to the release cadence |
Scope of work
What outsourced QA covers
Some of this is deep enough to have its own page. The rest lives here, because it is part of the same engagement.
Test strategy and planning
What release confidence means for your product, agreed before anyone writes a test case.
Manual testing
Exploratory and scripted testing by engineers who learn your product, not a checklist.
Automated testing
Suites that run on every pull request, so checking a release stops scaling with the product.
Performance testing
Load, stress and endurance testing against targets agreed up front.
Regression testing
Every production defect becomes a test case, so the same bug cannot ship twice.
Release validation
A go or no go on each release candidate, with the evidence behind it.
API testing
Contract and behaviour testing at the service boundary, run in CI.
Web and mobile coverage
Cross browser and real device coverage, against the matrix your analytics justify.
Accessibility testing
WCAG conformance as part of release validation, not a late separate audit.
Deliverables
What the engagement includes
The disciplines are below. This is what you get around them, and it is the part that decides whether outsourced QA actually reduces your risk or just adds people.
Every one of these is a commitment we make before starting, not a deliverable we describe afterwards. If any of them does not fit how your team works, that is a conversation to have during scoping rather than a surprise in week three.
A named QA lead accountable for the release callA test strategy agreed before anyone writes a caseTest cases documented and maintained in your tooling, not oursDefects reported with reproduction steps and a severity you can act onCoverage reporting on an agreed cadence, gaps includedThe suite integrated into your pipeline, so tests gate the releaseA go or no go on each release candidate, with the evidence behind itHandover documentation, so the suite outlives the engagement
Tooling
The testing stack we actually work in
We work in your stack where you already have one, because a QA engagement that starts by replacing your tooling spends its first month on migration instead of coverage. Where there is no stack yet, this is what we reach for: Selenium for browser automation, Postman for API testing, and Qase for test management, so cases, runs and defects live in one place rather than in a spreadsheet.
Whatever the tools, the suite runs in your pipeline. Tests execute on every pull request and on every release candidate, and the result is a gate rather than a report somebody remembers to read. That is the difference between having tests and having coverage you can trust on a Friday afternoon.
Reporting
How coverage is measured and reported
Most QA reporting counts activity: tests run, bugs logged, hours spent. None of that answers the only question you actually have, which is whether this release is safe to ship. So we agree the measures before we start, and we report against those.
- Which business critical flows are covered, and which are knowingly not.
- Defects found, with severity and what each one blocks.
- Escaped defects, meaning anything that reached production and should have been caught.
- Regression suite health: what runs on every release, what is flaky, what was quarantined and why.
- The gaps we have not closed yet, stated plainly rather than left out.
The last line matters more than the rest. A coverage report that only shows what is covered is a marketing document. Naming the gaps is what lets you decide whether a release goes out, and it is the part most QA vendors leave off.
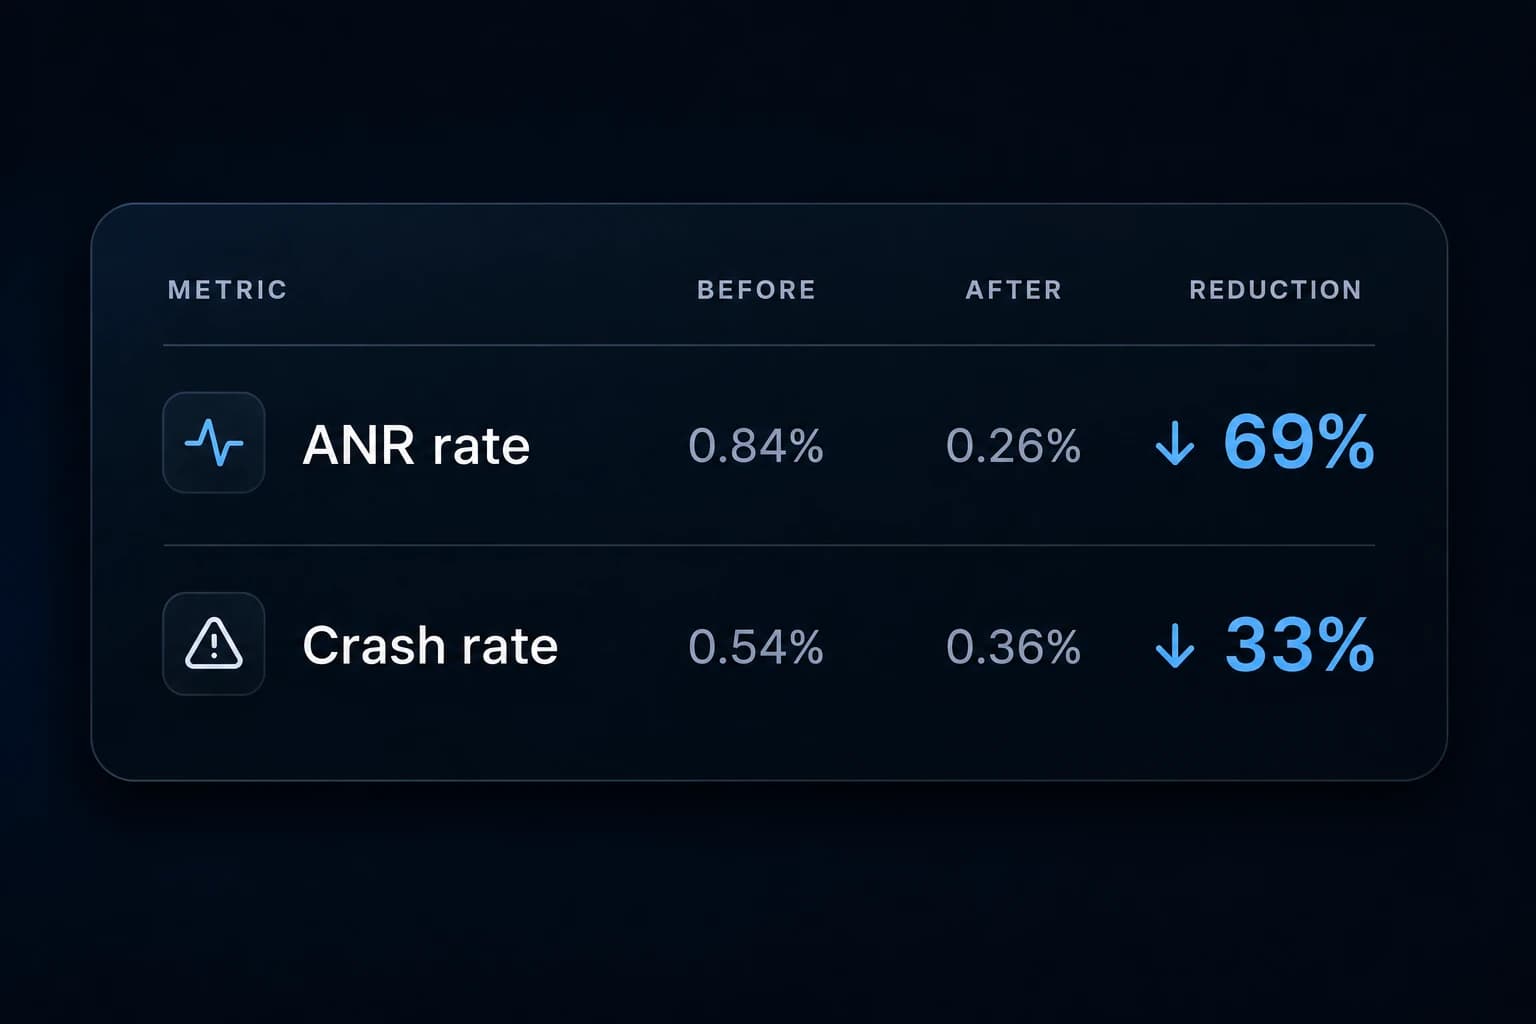
We hold our own work to the same measurement standard. In one Android engagement, the user-perceived crash rate fell from 0.54% to 0.36%, about 33%, while the user-perceived ANR rate fell from 0.84% to 0.26%, about 69%. Read the Android stability case study.
Process
How an engagement starts
- 01
Discovery
We start by understanding your product, release process, current QA capacity, known issues, and quality risks.
- 02
Test planning
We define the testing scope, critical workflows, devices, browsers, release criteria, and acceptance criteria.
- 03
Test cases
We create or improve test cases based on product behavior and business priorities.
- 04
Manual QA
Our QA team executes testing, documents issues, and reports bugs with clear reproduction steps.
- 05
Bug validation
We collaborate with developers and project managers to validate fixes, report QA risks, and track release readiness.
- 06
Regression & automation
We help improve QA coverage over time through regression testing, test coverage review, and automation planning where useful.
The early sequence matters more than the tooling. Scoping and test planning come before execution so the first cases target real risk instead of generic coverage, and the regression suite is built from what we actually find rather than from a template. How quickly each step lands depends on your release cadence and how much test material already exists, and we agree that in scoping rather than promising it here.
Roles
Roles that may support this service
QA EngineerQA Automation EngineerManual QA TesterProject ManagerFrontend DeveloperBackend DeveloperFull-Stack DeveloperTech Lead
Final roles are recommended after discovery.How we engage: three nearshore models
Discovery before SOW
Discovery comes before every reliable statement of work.
Before we recommend roles, timelines, or pricing, we need to understand your goals, technology stack, product situation, scope, risks, and constraints. Discovery helps us align expectations and create a realistic statement of work.
What discovery documents
- Business goals
- Product goals
- Technology stack
- Current situation
- Required roles
- Timeline expectations
- Budget expectations
- Risks and unknowns
- Success criteria
QA case studies and guides
All QA resources Articles
QA as a service vs in-house vs staff augmentation: how to choose
A build-vs-buy framework for choosing between QA as a service, in-house QA, and staff augmentation, plus a readiness score, red flags, and questions to ask before you commit.
QA & release
 Articles
How to evaluate QA testing services: a vendor selection guide
The criteria that separate real QA partners from checkpoint vendors, plus a scorecard to rate them, red flags to watch for, and the questions to ask before you sign.
QA & release
 Case study
How we reduced an Android app's crash rate by 33% and ANR rate by 69%
A focused Android stability effort reduced the app’s user-perceived crash and ANR rates by 33% and 69%, respectively.
QA & releaseEngineering
FAQ
Questions about this service
Yes. We can help define the QA process, create test cases, document bugs, validate releases, and recommend the right testing approach for your product.
We can support manual QA, regression testing, release validation, and QA automation planning or implementation depending on your product, goals, and current testing maturity. Explore our automated testing service
Yes. Our QA engineers can collaborate with your internal developers, product team, or existing vendor to improve testing coverage and release confidence.
We prioritize testing based on business-critical workflows, user impact, known risks, release goals, production issues, and areas where bugs could create the most damage.
Yes. NetForemost can add QA engineers to support your existing development team, improve testing coverage, document issues, validate releases, and strengthen your QA process without requiring you to build a full internal QA team.
Yes. NetForemost supports nearshore QA testing for teams that need better release confidence, clearer bug reporting, regression testing, cross-browser and cross-device coverage, and QA collaboration across distributed workflows.
QA engineers can start once scope and access are agreed. The first days go to reading your product, your existing tests if you have any, and your release process, so the first test cases target real risk instead of generic coverage.
You do. Test cases, automation code, and reporting live in your repositories and your tools, so nothing is locked to us. If the engagement ends, your team keeps a working suite and the documentation behind it.
We work in your existing stack where you have one. Where you do not, we commonly use Selenium for browser automation, Postman for API testing, and Qase for test management, and we integrate the suite into your pipeline so tests run on every pull request.
You get a written report on an agreed cadence: what was tested, what passed, the defects found with their severity, and where coverage still has gaps. The metrics are agreed before we start, so the report answers whether a release is safe rather than counting activity.